
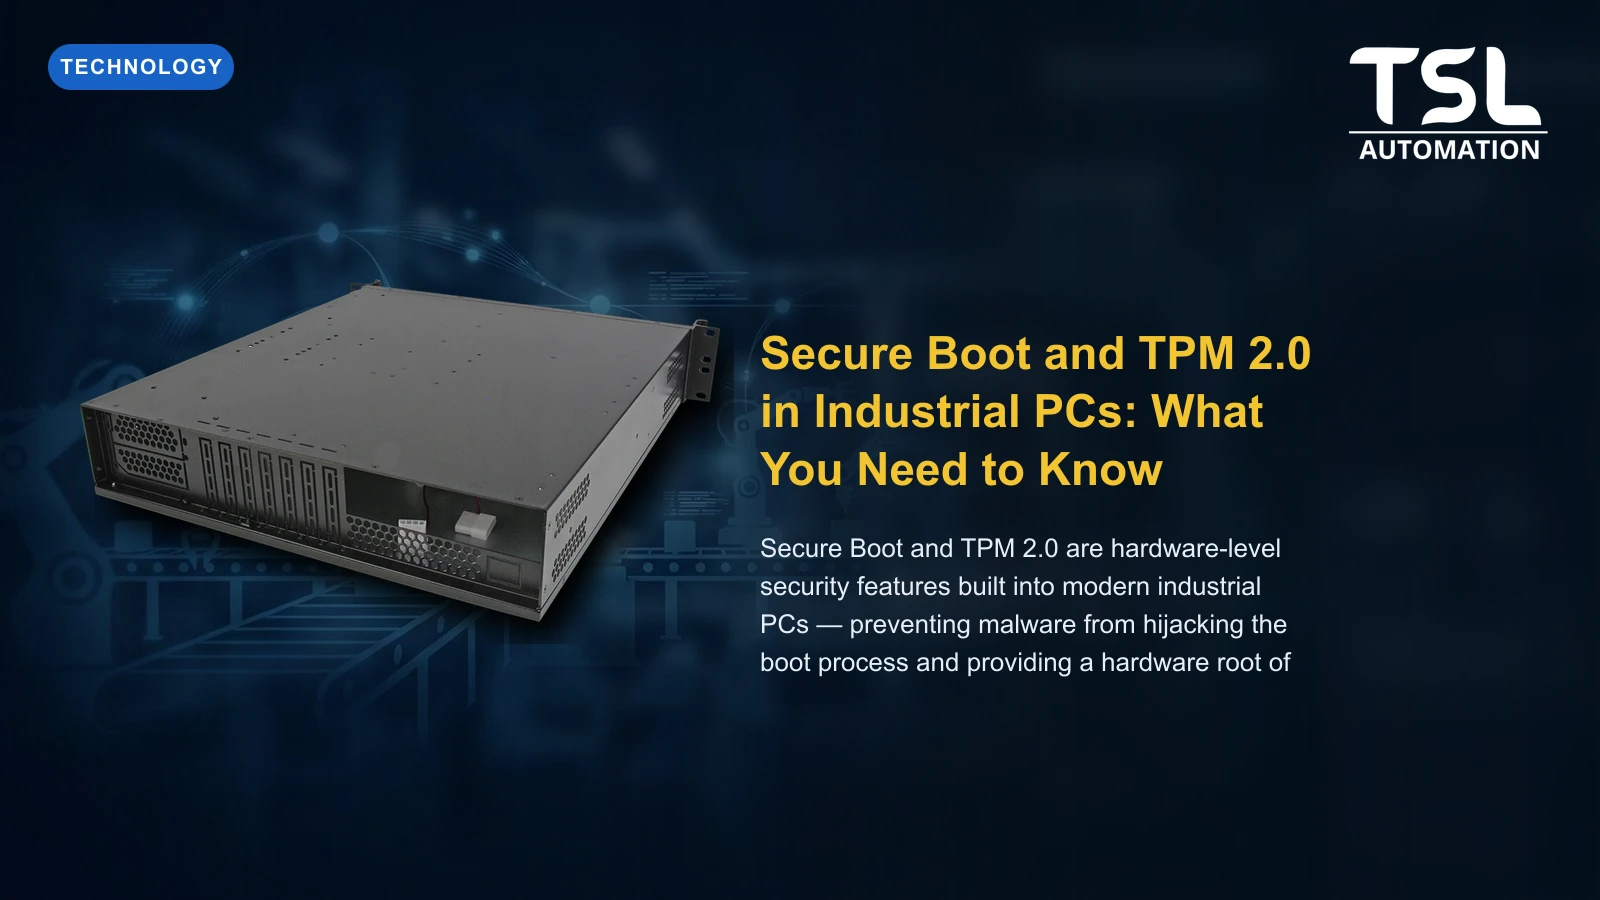
Secure Boot et TPM 2.0 dans les PC industriels : ce qu'il faut savoir
Sommaire
What Is Secure Boot?
Secure Boot is a UEFI firmware feature that verifies the cryptographic signature of every piece of software loaded during the boot process, bootloader, OS kernel, and drivers. If any component has been tampered with or replaced by malware (such as a rootkit or bootkit), Secure Boot blocks the boot and alerts the operator. This prevents the most persistent and damaging form of malware from surviving system restarts.
What Is TPM 2.0?
A TPM (Trusted Platform Module) is a dedicated security microcontroller embedded in the motherboard that provides hardware-level cryptographic services. TPM 2.0 stores encryption keys, certificates, and platform measurements in tamper-resistant hardware, ensuring that even if an attacker has physical access to the drive, encrypted data cannot be read on a different machine.
Why Industrial PCs Need These Features
- Ransomware protection, BitLocker full-disk encryption (requires TPM 2.0) makes stolen drives unreadable
- Supply chain security, Secure Boot prevents compromised firmware from running even if the storage was tampered with during shipping
- IEC 62443 compliance, hardware security features are increasingly required in industrial cybersecurity audits
- Remote attestation, TPM can prove to a remote server that the device has not been modified
Avalue Industrial PCs with TPM 2.0
All modern Avalue industrial motherboards and Panel PCs include a TPM 2.0 chip and UEFI Secure Boot support, available from TSL Automation. Enable Secure Boot and BitLocker for all SCADA workstations and industrial HMI PCs as a baseline cybersecurity measure.
Questions fréquentes
TSL Automation Solutions
Responsable marketing, TSL Automation Solutions
Sanjana couvre les tendances de l'automatisation industrielle, les lancements de produits et les analyses technologiques pour TSL Automation Solutions, distributeur basé à Mumbai d'IHM, de Panel PC et de systèmes informatiques embarqués au service des industriels en Inde et dans le monde.
Besoin d'aide pour choisir le bon produit ?
Notre équipe à Mumbai peut vous recommander l'IHM, le Panel PC ou le système embarqué adapté à votre application.
Contacter TSL AutomationArticles associés
IA embarquée ou IA cloud dans l'industrie : latence, bande passante et coûts réels
17 août 2026
NPU, GPU ou CPU : quelle puce pour votre charge d'IA embarquée ?
17 août 2026
Flambée des prix de la mémoire en 2026 : ce que la hausse de la DRAM change pour les acheteurs
17 août 2026