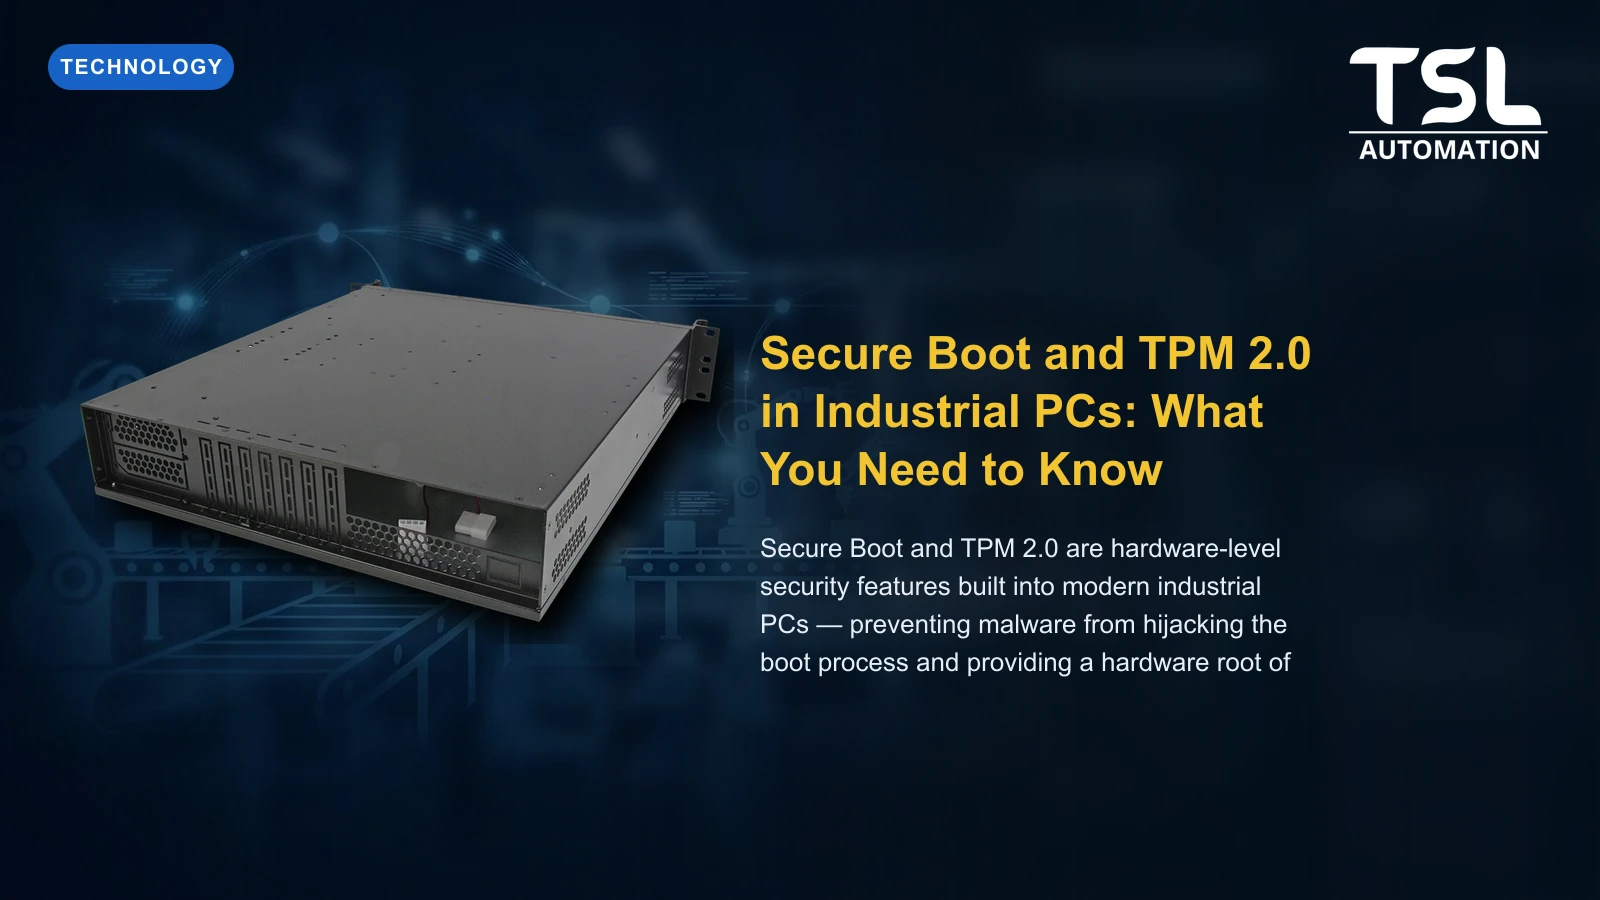
Secure Boot i TPM 2.0 w komputerach przemysłowych: co warto wiedzieć
Spis treści
What Is Secure Boot?
Secure Boot is a UEFI firmware feature that verifies the cryptographic signature of every piece of software loaded during the boot process, bootloader, OS kernel, and drivers. If any component has been tampered with or replaced by malware (such as a rootkit or bootkit), Secure Boot blocks the boot and alerts the operator. This prevents the most persistent and damaging form of malware from surviving system restarts.
What Is TPM 2.0?
A TPM (Trusted Platform Module) is a dedicated security microcontroller embedded in the motherboard that provides hardware-level cryptographic services. TPM 2.0 stores encryption keys, certificates, and platform measurements in tamper-resistant hardware, ensuring that even if an attacker has physical access to the drive, encrypted data cannot be read on a different machine.
Why Industrial PCs Need These Features
- Ransomware protection, BitLocker full-disk encryption (requires TPM 2.0) makes stolen drives unreadable
- Supply chain security, Secure Boot prevents compromised firmware from running even if the storage was tampered with during shipping
- IEC 62443 compliance, hardware security features are increasingly required in industrial cybersecurity audits
- Remote attestation, TPM can prove to a remote server that the device has not been modified
Avalue Industrial PCs with TPM 2.0
All modern Avalue industrial motherboards and Panel PCs include a TPM 2.0 chip and UEFI Secure Boot support, available from TSL Automation. Enable Secure Boot and BitLocker for all SCADA workstations and industrial HMI PCs as a baseline cybersecurity measure.
Często zadawane pytania
TSL Automation Solutions
Dyrektor marketingu, TSL Automation Solutions
Sanjana pisze o trendach w automatyce przemysłowej, premierach produktów i nowych technologiach dla TSL Automation Solutions, dystrybutora paneli HMI, paneli PC i systemów wbudowanych z siedzibą w Mumbaju, obsługującego producentów w Indiach i na całym świecie.
Potrzebna pomoc w wyborze właściwego produktu?
Nasz zespół w Mumbaju doradzi odpowiedni panel HMI, panel PC lub system wbudowany do Państwa zastosowania.
Kontakt z TSL Automation